Six layers. A capability is complete when it meets all six.
Five layers of knowledge, from general to team.
Knowledge comes from three sources: expert judgement, regulation and the institution itself.
- Regulation applies at every level.
- A team may tighten an institution's rule and may not relax it.
Counterparty risk, continuous and auditable.
The counterparty credit risk cockpit works from one view of every counterparty, one library of historical events and one policy for when the system acts and when it asks.
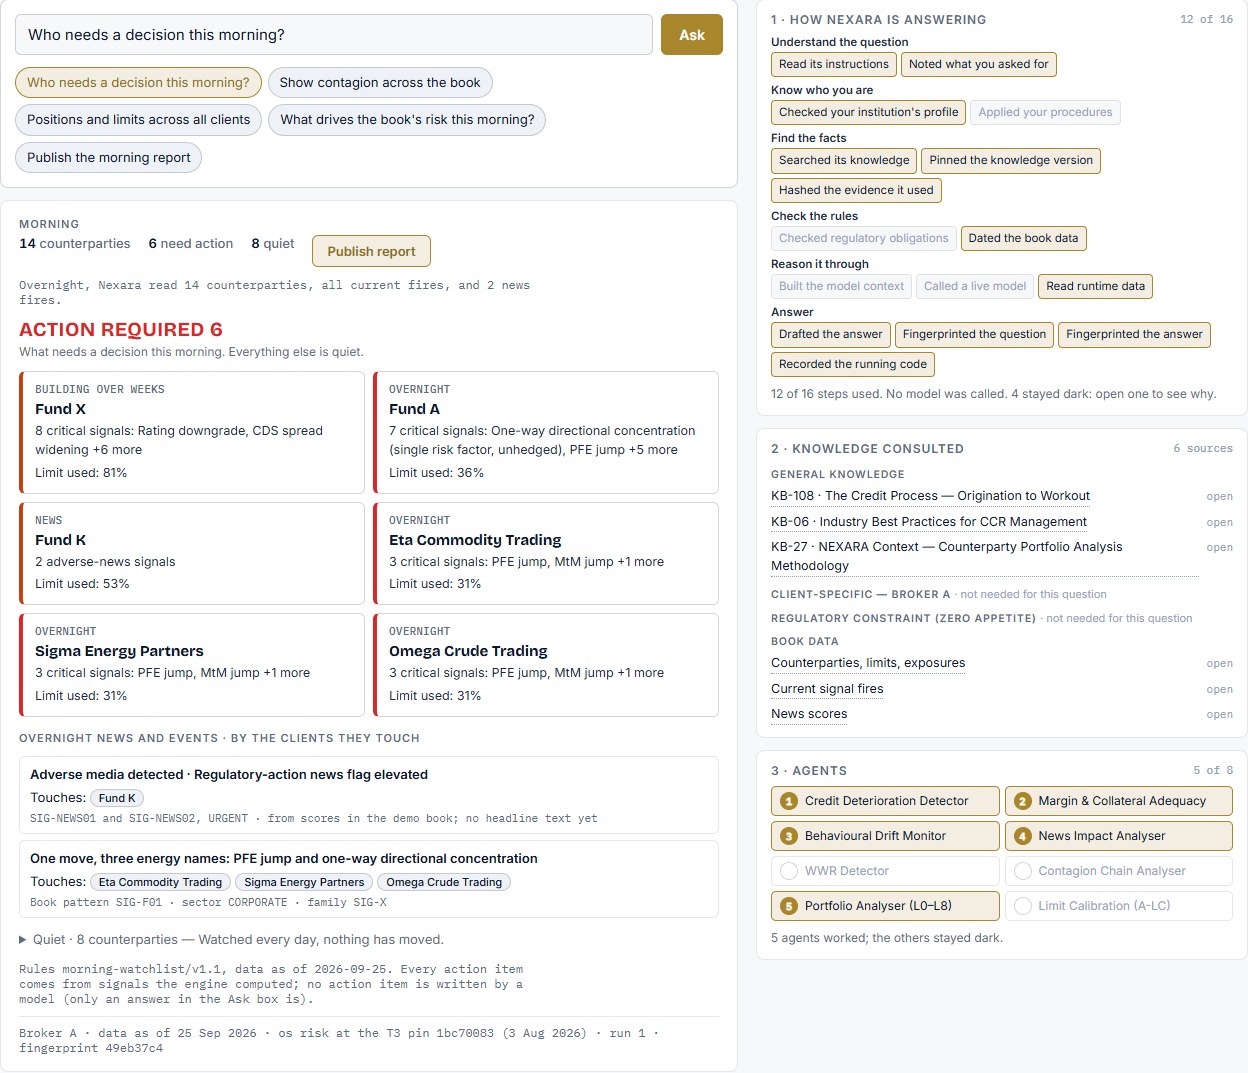
Morning brief
The daily head-of-CCR view: what changed overnight, which counterparties need attention and what the system already handles.
Counterparties
One card per counterparty with its risk profile, historical pattern match, known limitations and the reasoning behind every alert.
Signals
Live indicators of distress across margin, credit, behaviour, exposure, markets, P&L and payments, monitored and explained.
Portfolio
Aggregate exposure, concentration and cross-counterparty correlation, shown in full and not hidden by netting.
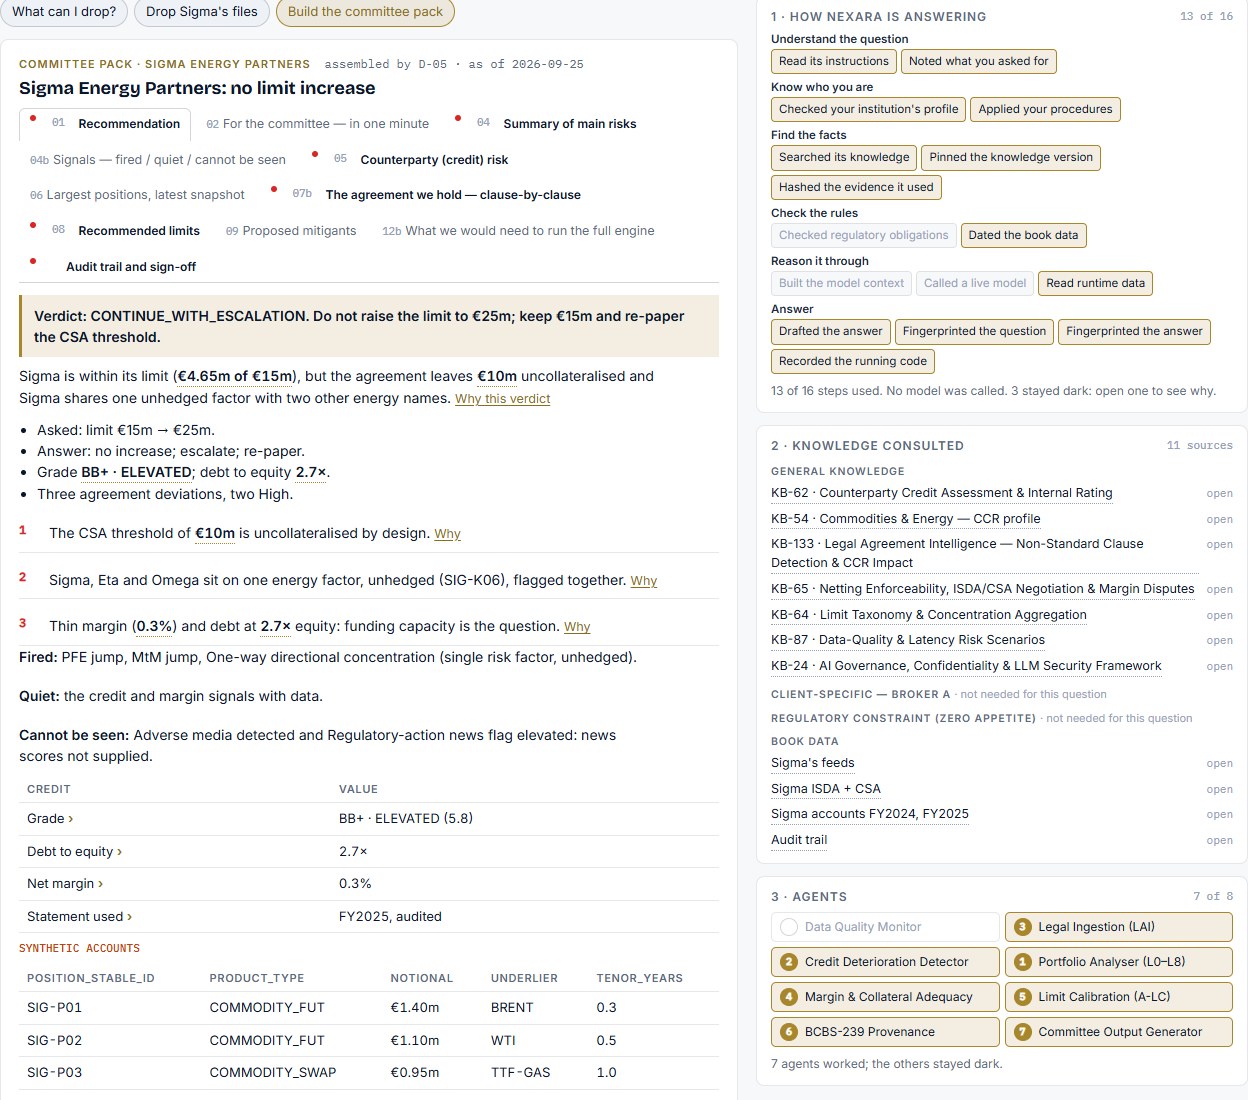
Limits
Limit monitoring, breach detection, utilisation trajectories, approvals and escalation.
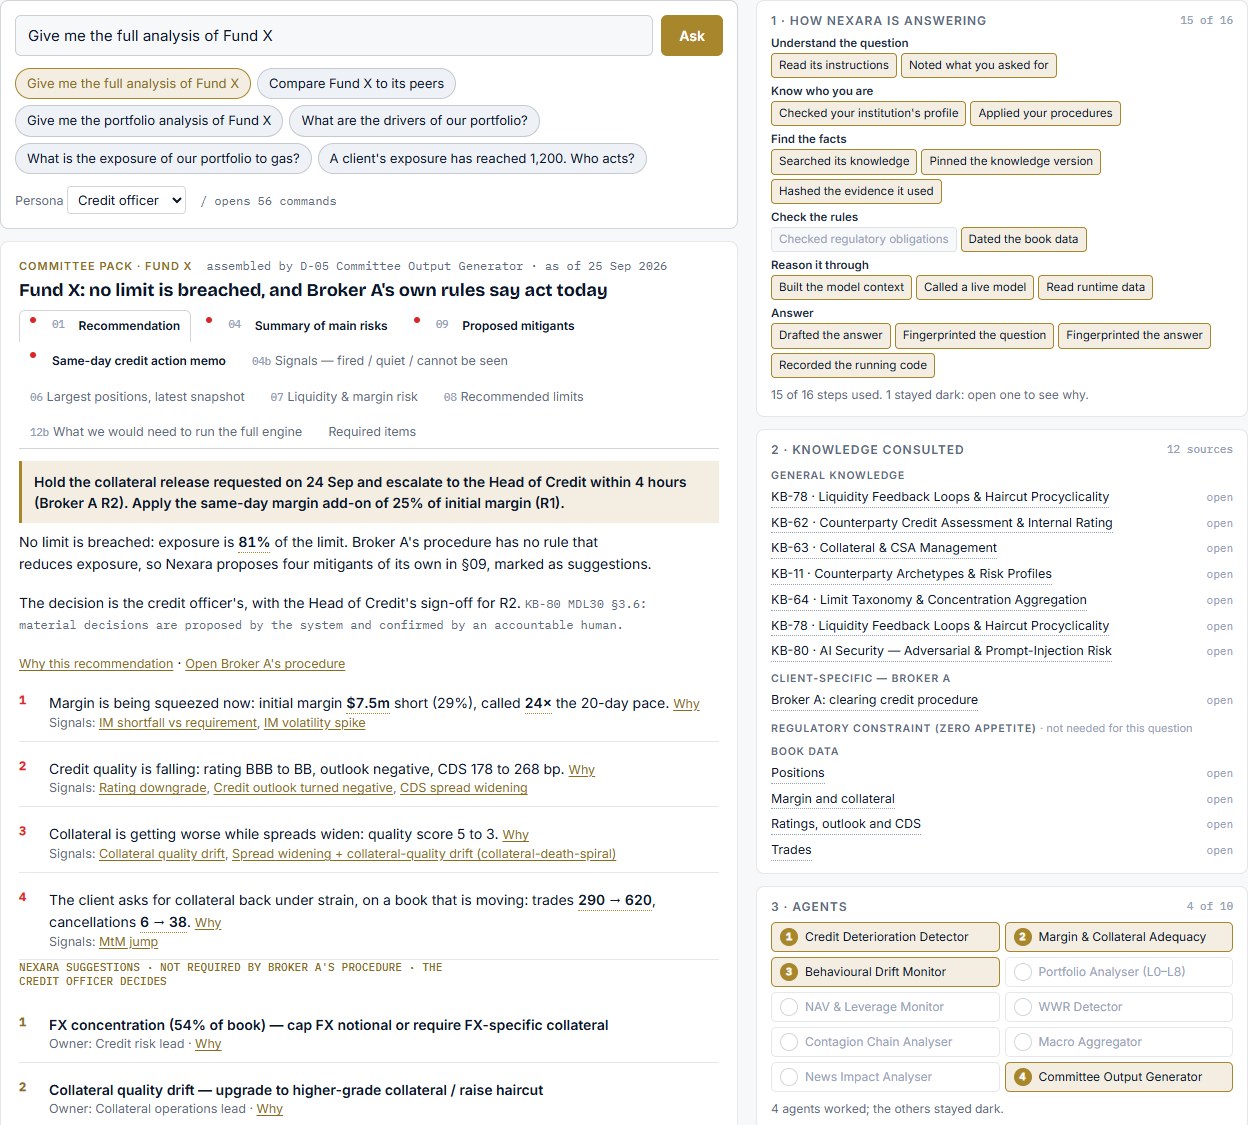
Ask Nexara
A conversational layer that explains any alert, counterparty or decision from the platform's data. Decisions stay with people.
Designed against the regulations that apply.
Each design choice maps to a supervisory requirement.
CRR3
The EU capital requirements framework, including counterparty credit risk.
Guidelines for counterparty credit risk management
The post-Archegos guidelines: actionable metrics, bespoke stress tests per counterparty and a register of known limitations.
US supervisory expectations
Models are validated, traceable and open to challenge.
Risk data aggregation
Data lineage from source feed to final decision. Every value is traced and every output reproducible.
EU AI Act, human oversight
Every automated output is classified for the operator as acting, recommending or asking.
UK model risk management
One design, reviewed in each jurisdiction.